Sellers trust Realify with their most sensitive business data, pricing strategies, inventory levels, margin structures, and customer order information. That trust demands transparency about how we handle it. This report is our commitment to plain-language disclosure.
What we access
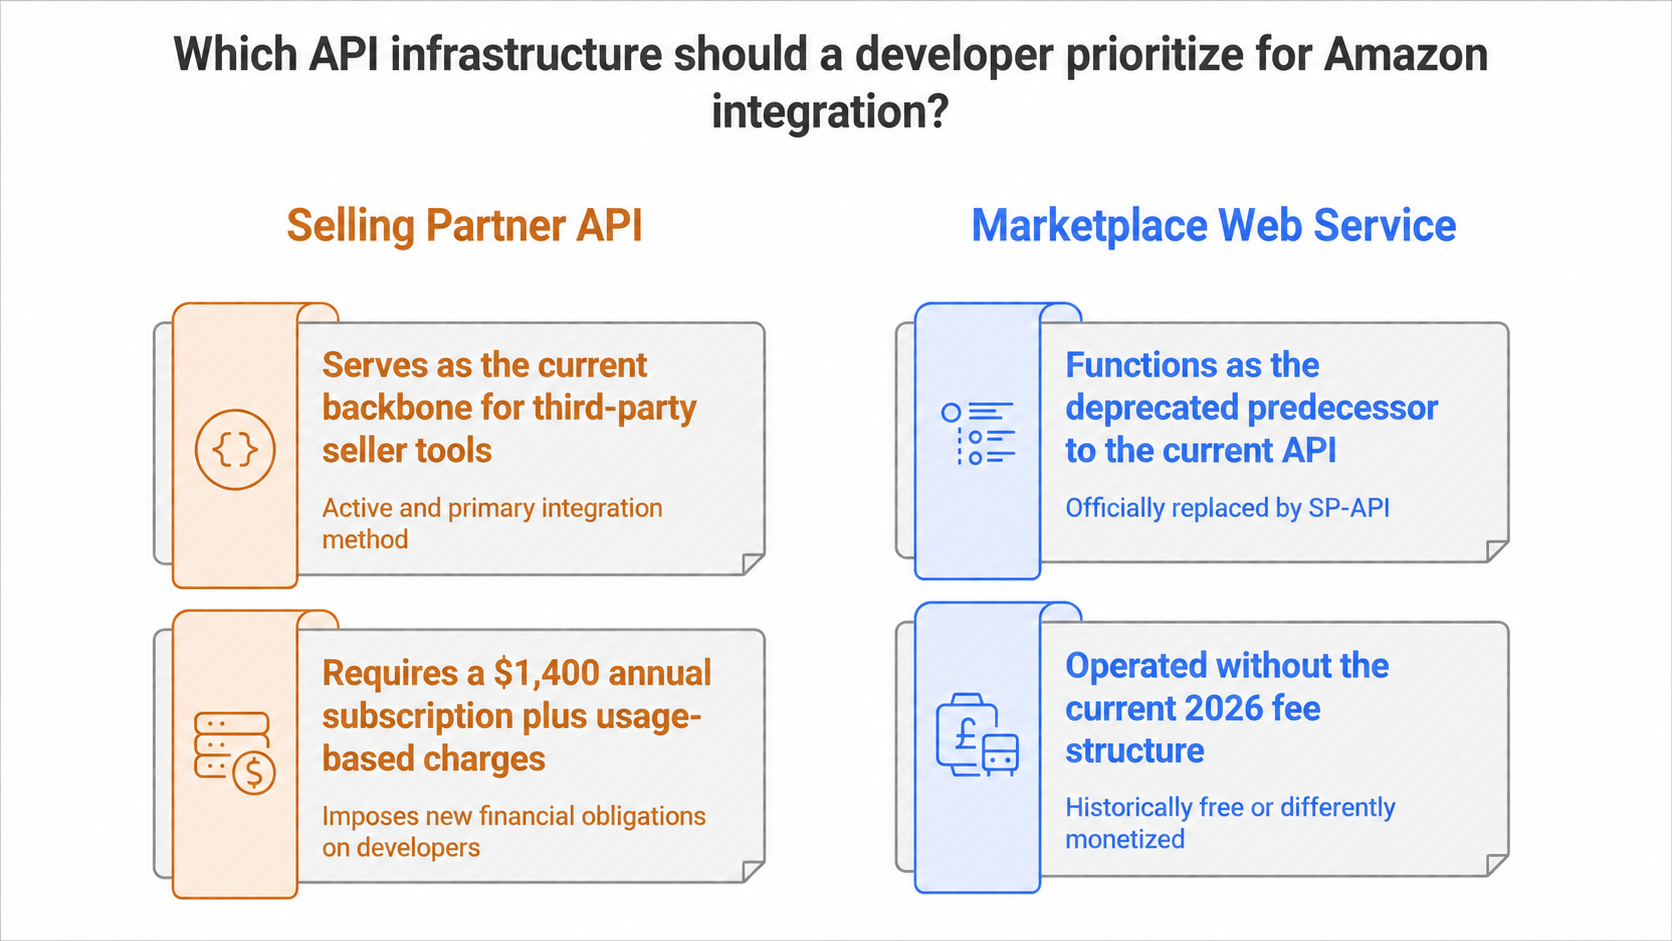
When you connect your Amazon account to Realify, you authorize access through Amazon’s official Selling Partner API (SP-API) using OAuth 2.0, Amazon’s standard secure authorization protocol. We never request, access, or store your Amazon Seller Central login credentials [1].
With your authorization, Realify accesses: product catalog and listing data (titles, descriptions, images, categories), inventory levels across fulfillment channels (FBA, FBM), pricing and competitive positioning data, order and financial settlement data, advertising campaign performance data, and seller account health metrics.
We access only the data categories required to provide the services you’ve subscribed to. An Explorer plan subscriber who uses only pricing intelligence generates fewer API calls than a Pro subscriber using the full platform.
How we process it
Your data is processed for one purpose: to generate intelligence, recommendations, and (where you’ve authorized) automated actions that improve your business operations.
We analyze pricing data to identify competitive opportunities and risks. We analyze inventory data to forecast demand and optimize allocation. We analyze advertising data to improve campaign efficiency. We analyze order data to calculate margin at the SKU level. We analyze all of these together to generate cross-domain insights that no single data source can produce.
We do not aggregate your data with other sellers’ data for benchmarking purposes. We do not use your data to train models that are then applied to other sellers’ businesses. We do not sell, license, or share your data with third parties for any purpose.
How we protect it
Data isolation: every Realify account operates in a fully isolated data environment. Your data is never co-mingled with data from other sellers at the infrastructure level. We use separate encryption keys per account.
Encryption: all data is encrypted in transit (TLS 1.2+) and at rest (AES-256). API communications with Amazon use the same encryption standards Amazon requires for SP-API integrations.
Access controls: internal access to customer data is governed by role-based access control with least-privilege enforcement. Access events are logged and retained for 12 months.
Infrastructure: Realify’s platform runs on enterprise-grade cloud infrastructure with 99.9% uptime SLA, automated backups, and disaster recovery procedures.
What we never do
We never access your Amazon Seller Central login credentials. We never share your data with other sellers or third parties. We never use your data to advantage competitors. We never scrape Amazon or use unauthorized access methods. We never retain your data after account termination beyond the export window (30 days) and secure deletion period (90 days total).
Your controls
You can revoke Realify’s API access at any time from Amazon Seller Central under Apps & Services > Manage Your Apps. Revocation immediately stops all data syncing.
You can request a full data export at any time while your account is active. You can request deletion of your data at any time, subject to legal retention requirements.
Compliance
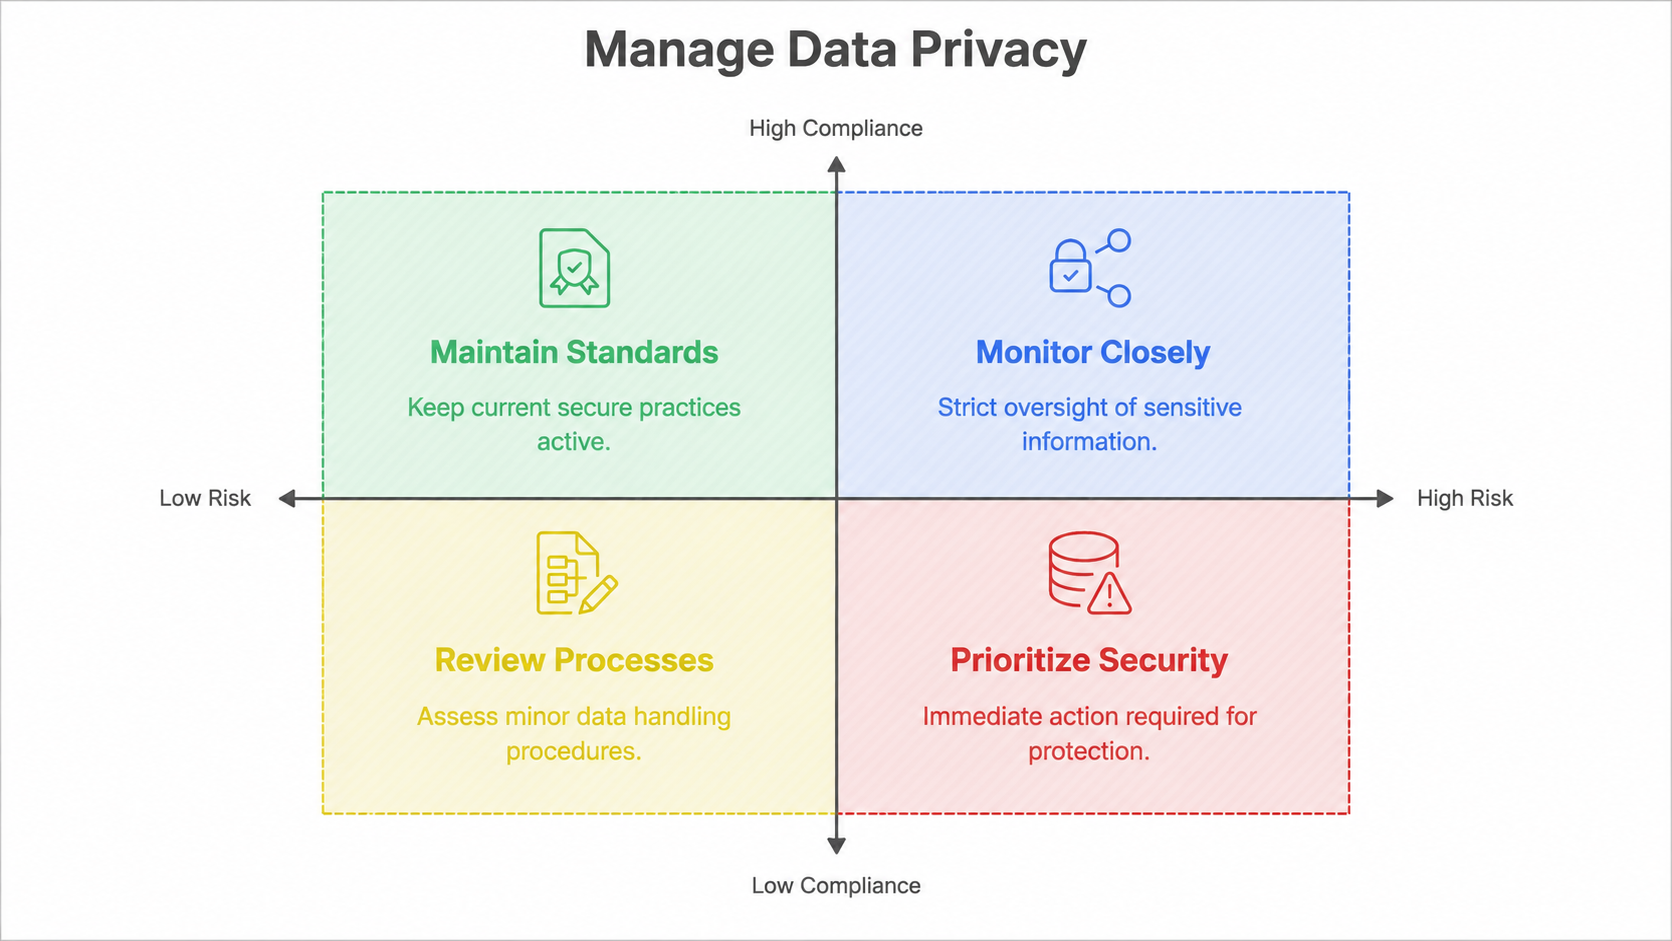
Realify is designed for compliance with: Amazon’s SP-API Developer Agreement and Acceptable Use Policy, the EU General Data Protection Regulation (GDPR), the California Consumer Privacy Act (CCPA), and the Indian Digital Personal Data Protection Act (DPDPA). A Data Processing Agreement is available for all customers.
For data-related inquiries: privacy@realify.ai.
- •[1] Amazon SP-API OAuth 2.0 authorization protocol documentation.